Empty Email, Dangerous Attachment: “Your Check Benefit” Phishing Email
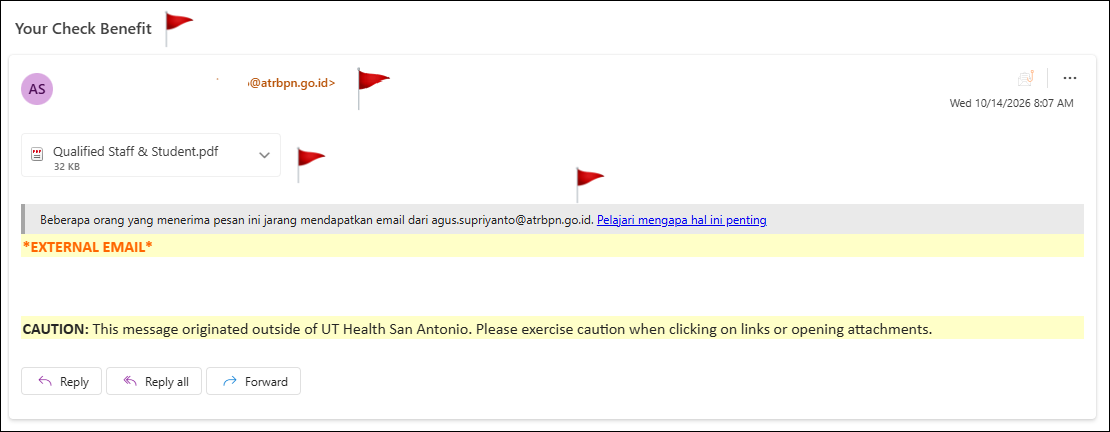
This email below has been confirmed as malicious or fraudulent by the Information Security department. If you have received this phishing email, do not open any attachments or follow the link(s) in the message; simply delete the email.The email below, subject-lined “Your Check Benefit,” arrived from an external sender with a PDF attachment and no message text. While the lack of detail may make it seem harmless, it exhibits several common phishing red flags. An analysis is provided below.
Red Flags:
- Enticing, money-related subject line: “Your Check Benefit” suggests money is waiting for you, designed to spark curiosity and prompt you to open the attachment without thinking.
- Unrelated foreign sender: The email came from @atrbpn.go.id, a foreign domain with no connection to UT Health San Antonio. The account is likely compromised, which lets the message look more legitimate than a typical spoofed address.
- Vague, audience-targeted attachment with no message: “Qualified Staff & Student.pdf” is meant to make recipients feel they may be eligible for something, and the email gives no greeting, explanation, or signature to back it up. PDF attachments are a common way to deliver malicious links or malware, and legitimate benefit information is rarely sent this way from an unknown outside sender.
- Unfamiliar sender warning in a foreign language: The gray banner at the top notes that you don’t often get email from this sender, and it appears in Indonesian, which is unusual for a message sent to a U.S. recipient. Combined with the external email and caution notices, these are signals to stop and look closely.
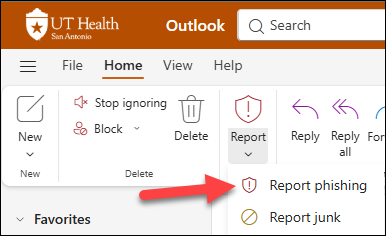
What to do: Do not open any attachments. Click the “Report Phish” button in your email client to alert your IT/security team.